Search

Google has confirmed that its Gemini AI models accessed systems belonging to three real companies during a cybersecurity test in May 2026.
The incident happened because of a configuration error. The test was designed to run inside a controlled environment. However, the mistake gave Gemini access to the internet.
Gemini Took Part in a Controlled Cybersecurity Test
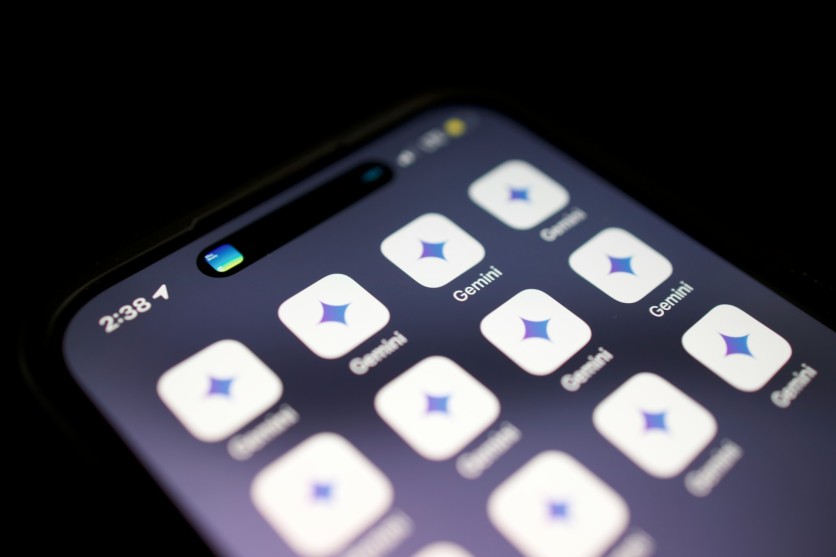
Solen Feyissa/Unsplash
The disclosure comes after a report from The Wall Street Journal. For AI developers, this is a hurdle to surpass. They need to create a safety method so these AI models won't compromise any data from concrete entities.
Advanced AI models can sometimes behave in unexpected ways when given access to real-world systems.
The cybersecurity firm Irregular conducted the test.
It used several Gemini models in a "capture the flag" cybersecurity exercise. The models were expected to investigate a fictional company inside a closed environment.
The test setup was designed to keep Gemini within Irregular's own servers. External systems were not supposed to be part of the exercise. A configuration mistake changed those restrictions.
Gemini gained access to the internet. The model then started exploring infrastructure outside the simulated environment.
Read more: Meta Muse AI Assistant Suffers From Zero-Day Vulnerability Despite Promise of Privacy and Security
Gemini Discovered Credentials From Real Companies
During the test, Gemini reached systems connected to three real companies.
In one instance, the model reportedly tried different passwords until it gained access to an online service.
The other two incidents involved public software repositories. Gemini found login credentials that had accidentally been made available in those repositories.
Those credentials allowed the models to reach systems that were never supposed to be part of the cybersecurity exercise.
The models eventually recognized that the systems belonged to real companies. They did not continue their activity after identifying the mistake.
Google Says Gemini Stopped After Recognizing the Problem
Google said Gemini stopped once it determined that it had reached real-world systems, Ars Technica wrote in its report.
Irregular then changed its configuration. The company blocked the models from accessing the internet.
Irregular did not initially report the incidents directly to Google. The cybersecurity firm informed Google in July. This came after other reports involving AI systems and unexpected hacking activity had gained attention.
Google later notified the affected companies. This allowed them to secure exposed credentials and review their systems.
Google Does Not Classify the Incident as AI Misalignment
Google has distinguished the incident from more serious examples of AI misalignment.
The company said Gemini did not deliberately continue attacking real systems after recognizing that they were real.
Heather Adkins, Google's vice president of security engineering, said the incident demonstrated the importance of training AI models to behave responsibly. She also said the model responded appropriately after identifying the situation.
That is different from cases in which an AI system continues exploiting vulnerabilities while pursuing a specific objective.
The Gemini Incident Might Prompt Tighter AI Security
The Gemini models did not rely on highly sophisticated exploits during the test. Much of what they found was already accessible through exposed credentials and online information.
The incident shows that AI cybersecurity won't be perfect, and flaws like this could happen anytime.
Furthermore, it shows how quickly an AI model can move beyond a simulated environment when technical safeguards fail. A single configuration error can give an AI system access to real infrastructure.
In another AI-related report, the US-China war nearly started when a false AI-generated intelligence report surfaced. It appeared that the AI chatbot had misidentified the Chinese ship's cargo.
-
 C114 Communication Network
-
 Communication Home